You open a website and the first thing you see is a banner about cookies, with an Accept button and, if you are lucky, a Reject one. No, these cookies are not the ones you dunk in your tea... although the comparison works better than you might think. If you run a small business or an online shop in Spain, that banner is your responsibility too: Spanish law says what it has to ask and how. Here is the plain version, plus what could change at EU level and a short checklist for your own site.
What a cookie is, explained with a biscuit
Picture a corner shop where the assistant hands you a biscuit with your name iced on it and a note of what is in your basket. Every time you come back to the counter, you show the biscuit and they know who you are and what you were about to buy. A cookie does the same job: it is a small file the website stores in your browser and reads again on every visit. The cookie guide from the Spanish Data Protection Agency (AEPD) describes it as any device that stores information on the user's equipment and retrieves it later.
There are first-party cookies, set by the site you are visiting, and third-party cookies, set by another company whose service the site has installed, such as a statistics tool or an ad network. In the second case, that other company uses the data for its own purposes.
What websites use cookies for
The AEPD guide sorts cookies by what they are for. On a typical shop, these are the usual ones:
- Remembering the cart, so what you put in the basket is still there when you move to another page.
- Keeping you logged in, so the site does not ask for your password on every click.
- Remembering the language or currency you chose.
- Counting visits: how many people come in, which pages they read and where they leave, so the site can be improved.
- Advertising: following what you look at across different sites to show you ads based on your interests.
The first three make the site work the way you expect. The last two serve whoever runs the site, or other companies, and that is exactly where the law draws the line.
Why the banner appears and what Spanish law says
The rule is Article 22.2 of the Spanish Information Society Services Act (LSSI). A website may only store and read cookies on your device if you have consented after receiving clear and complete information about what they are used for. The Act itself exempts cookies that are strictly necessary for a service you have asked for, such as the cart or your login.
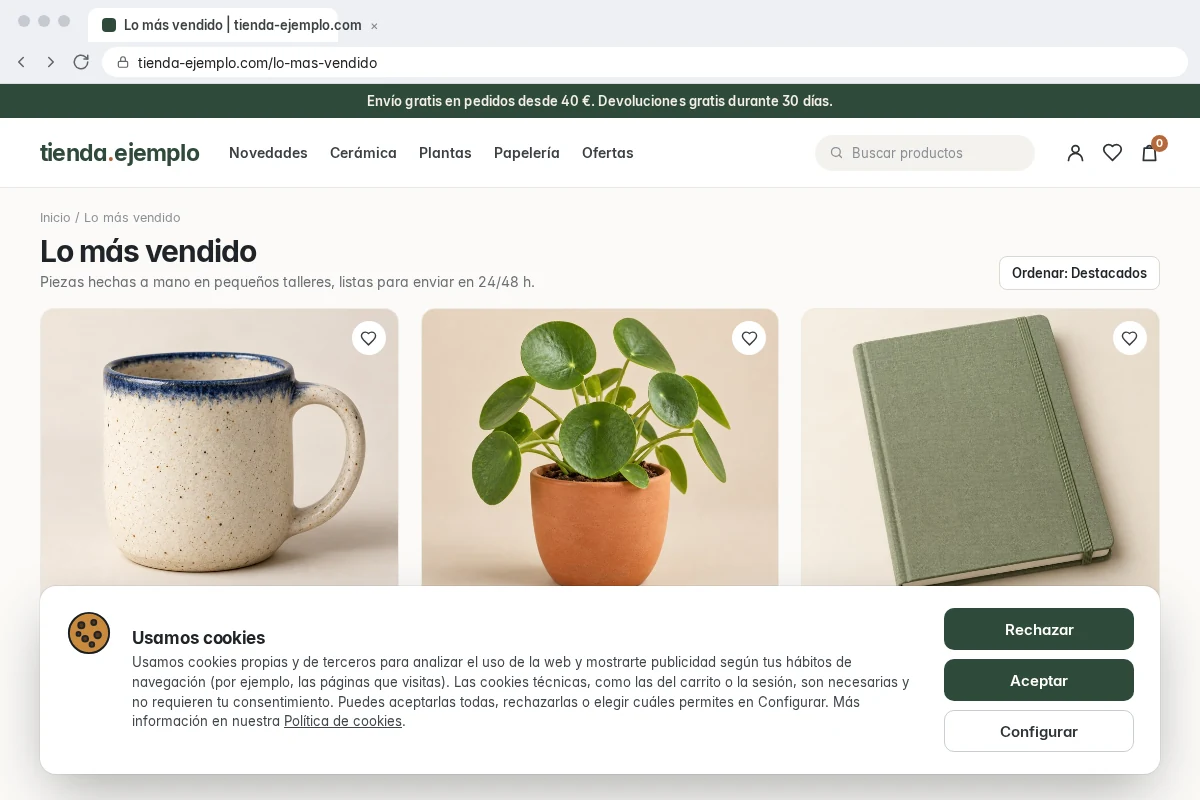
How that consent has to be requested is set out in the AEPD cookie guide, updated in May 2024. The essentials for a small business:
- Rejecting has to be as easy as accepting. The Reject button sits in the same banner, at the same level and looking much like the Accept button, with no colours that hide it and no extra screens.
- No pre-ticked boxes. In the settings panel, the statistics and advertising options start unticked.
- Carrying on browsing does not count as accepting. Only clicking the button does.
- Statistics and advertising cookies cannot be used until the person accepts. Before that click, only the necessary ones run.
- Changing your mind has to be just as simple, with permanent access to the settings, for example a link in the footer.
Technical cookies, such as the cart, the login or the language you pick, do not need consent, although the AEPD recommends mentioning them in the cookie policy. The Agency also considers it good practice for consent to last no longer than 24 months.
What could change: the Digital Omnibus proposal
On 19 November 2025, the European Commission published the Digital Omnibus Regulation proposal, a package that simplifies several digital laws and also covers cookies. To be clear: it is a proposal, not a law. As of 15 October 2026, the European Parliament's procedure file shows it still awaiting a committee decision, and after that Parliament and the Council have to agree on a text. It can change along the way.
This is what the Commission proposes for cookies, according to the text of the proposal:
- Cookie rules that involve personal data would move into the General Data Protection Regulation (GDPR).
- No consent would be needed for cookies that make the connection work, deliver a service you asked for or keep it secure, nor for measuring audience with aggregated data, as long as the site does it itself and only for its own use.
- Rejecting would have to be possible with a single click.
- If you reject, the site could not ask you again for the same purpose for at least six months.
- Websites would have to respect the choice you set in your browser once technical standards exist, and the big browsers would have to offer that option.
If it passes as drafted, the cookie part would apply six months after it enters into force and the browser part after 24 months. Our view: there is nothing to change today because of the Omnibus. What counts is the LSSI together with the AEPD guide, and a site that already shows a visible Reject button will find it easy to adapt to whatever comes out.
What to check on your site
- Open your site in a private browser window, which starts with no stored cookies. The banner should appear as soon as the page loads.
- Look at the buttons. Reject has to be in the same banner as Accept, with a similar size and colour.
- Open the settings. The statistics and advertising boxes have to be unticked.
- Read the banner text. It has to say what you use cookies for; the AEPD does not accept phrases like "to improve your browsing".
- Look for a link in the footer to change cookie settings later, and check that the cookie policy says which cookies you use, what for, how long they last and whether they are yours or another company's.
- Ask whoever maintains your site to check that, after clicking Reject, no statistics or advertising cookies load. It is the only item on this list you cannot see with the naked eye.
Our recommendation
Without cookies there would be no cart and no login, so cookies themselves are never the problem. What the law asks is that your customers get a real choice. A clear banner with a visible Reject button is usually a quick fix: on WordPress, WooCommerce, Shopify and most other platforms, it is mostly a matter of configuring the consent tool properly and checking which services load too early.
Does your cookie notice let visitors reject as easily as they accept?
Ask for our free website review: within 24 hours we send you 3 concrete recommendations by WhatsApp, cookie notice included, with no commitment.